French President Emmanuel Macron confirmed during a joint television appearance on TF1 and France 2 that authorities must actively consider the possibility of a direct Russian attack on a French airport, warning that geopolitical tensions are escalating sharply.
Secret Government Assessments Outline Potential Russian Escalation Scenarios
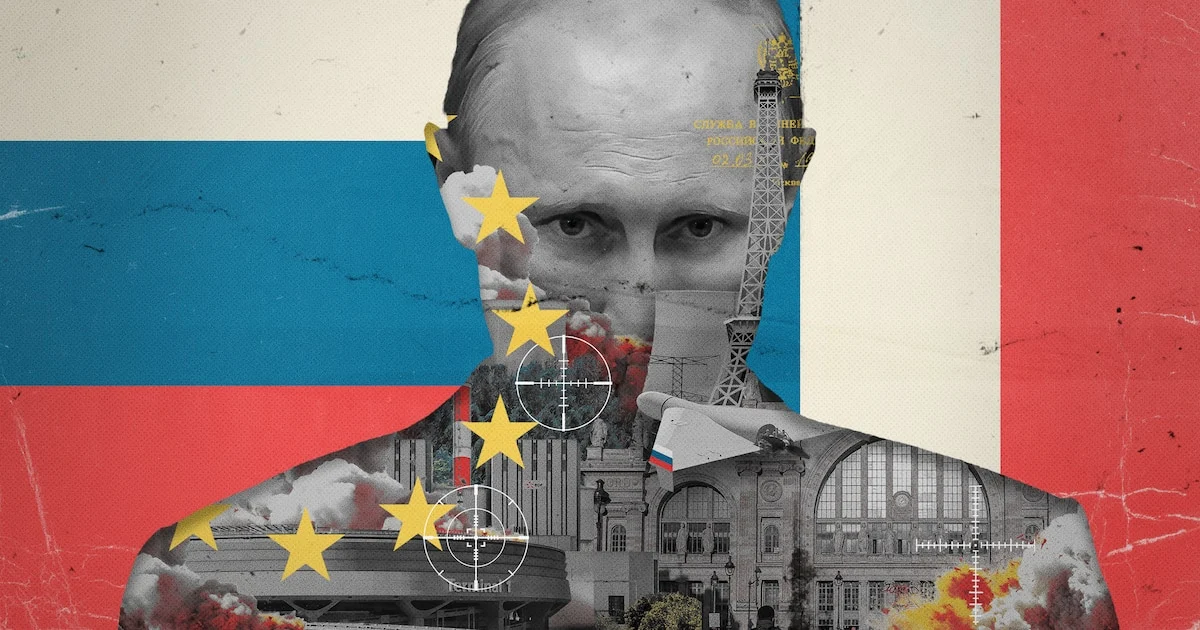
A confidential government note prepared in September 2026 for an Elysee Palace meeting details various threat scenarios compiled from French intelligence reports. According to the document, the most probable trajectory involves an escalation of hybrid attacks heading into early 2027. The assessment lists potential actions ranging from infrastructure sabotage and cyber offenses to terrorist actions causing civilian casualties or electronic jamming capable of bringing down a civil aircraft. French officials indicate that Vladimir Putin has authorized intelligence services to project violence directly onto European soil, driven by frustration over the stalled front lines in Ukraine and domestic economic pressures.
The Leipzig Airport Precedent and European Security Alarms
European intelligence agencies heightened their alert levels following a failed drone attack at Germany’s Leipzig airport during the night of August 4 to August 5. Security sources confirmed that a drone equipped with 800 grams of explosives and a SIM card designed to mimic mobile phone tracking targeted a Ukrainian cargo plane loaded with munitions. While the triggering mechanism malfunctioned and prevented detonation, German authorities recovered DNA evidence linking the operation to an individual connected with Russia’s military intelligence agency, the GRU. Clément Renault, a researcher at the Institute for Strategic Research at the Military School, noted that as the front lines remain frozen, Moscow views Europe as the strategic depth of Ukraine.
Cyber Threats and Defense Industry Vulnerabilities
French cybersecurity authorities have also tracked a qualitative and quantitative surge in Russian cyber operations. While France has largely avoided major disruptions—partly due to warnings that Paris possesses powerful cyber retaliation capabilities—second-tier government notes highlight that hackers from Russia’s FSB internal intelligence are increasingly tasked with remote sabotage. An expert with France’s national cybersecurity agency, ANSSI, expressed particular concern over potential supply-chain attacks targeting small and medium-sized defense contractors through professional software channels, echoing the widespread disruption caused by the NotPetya cyberattack in June 2017.
Broader Societal and Overseas Disruptions
Beyond traditional military targets, French security preparations anticipate attempts to disrupt core societal functions through the sabotage of critical energy, transport, and telecommunication networks. The General Secretariat for Defence and National Security has previously flagged risks of foreign interference in French overseas territories, including potential exploitation of decolonial tensions in New Caledonia and the Antilles, migration pressures affecting Mayotte, and territorial disputes surrounding the Scattered Islands by supporting Madagascar. While past operations in Europe frequently relied on low-level expendable agents recruited via the internet, officials warn that future actions may feature more professionalized cells modeled on the Leipzig infiltration tactics.
Keep reading