European Union Warnings Over Supermarket Refrigeration Cyberattacks
“Sens dubte no són fets aïllats, i hem de reforçar col·lectivament la nostra resiliència i preparació davant d’aquesta mena d’incidents cibernètics,” said European Commission spokesperson Thomas Regnier, addressing a coordinated wave of cyber intrusions targeting food retail infrastructure across the continent, ara.cat reported.
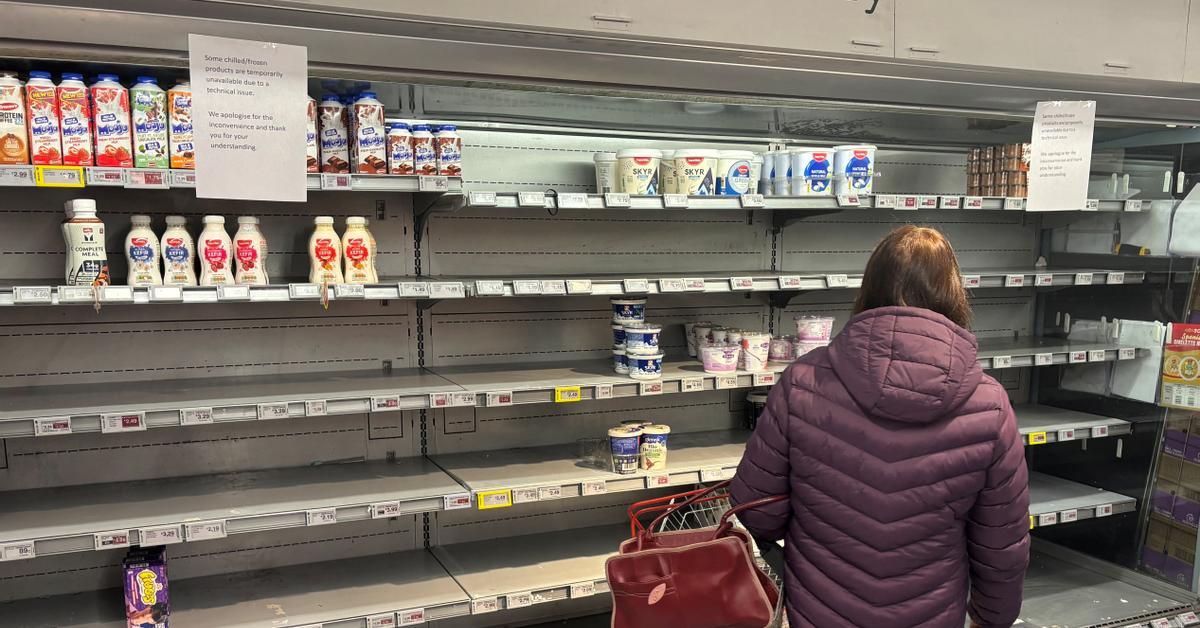
The European Union has formally warned that ongoing digital assaults on supermarket refrigeration systems represent a systemic threat rather than isolated incidents, prompting Brussels to convene emergency coordination meetings. The cyber intrusions have impacted food retail chains across eight European nations, disrupting critical supply chains and forcing stores to discard tons of spoiled food.
Eight Countries Impacted by Coordinated Remote Freezers Tampering
The malicious campaign first surfaced in earnest when establishments in Belgium, Sweden, the Netherlands, Luxembourg, Ireland, Finland, and Estonia reported sudden digital disruptions. Portugal became the eighth affected nation after seven stores belonging to the Intermarché chain suffered severe refrigeration failures.
According to the Grupo Mosqueteiros, which operates the Portuguese brand, the cyberattack bypassed individual storefronts to target an external third-party vendor responsible for maintaining and managing the refrigeration equipment. The breach caused temperatures inside storage units to spike dramatically in some international markets, with hackers manipulating electronic controllers remotely to push freezer temperatures up to 50 degrees Celsius.
Brussels Convenes Emergency Security Coordination Meetings
In response to the multi-country crisis, the European Commission convened two high-level coordination meetings involving key security bodies, including the European Union Agency for Cybersecurity (ENISA) and Europol. Officials also utilized the EU-CyCLONe network to connect directly with national authorities across the affected member states.
The primary objective of these sessions is sharing threat intelligence and designing a unified collective defense strategy. European officials remain cautious regarding attribution, noting that determining whether state actors are behind the operations remains the responsibility of national police forces conducting criminal investigations.
Retail Brands Suffer Financial Losses from Ruined Inventory
Major international retail brands—including Delhaize, Carrefour, Spar, Swedish chains ICA and Coop, and select Ikea stores—have reported multi-million-dollar losses due to ruined inventory. Affected companies have scrambled to deploy refrigerated trucks to salvage perishable goods and activate emergency operational plans.
Civil society groups, such as Citizens for Cybersecurity, have called for urgent mandatory security audits across major distribution networks. Security analysts point out that many industrial refrigeration controllers remain exposed directly to the internet without adequate firewall protections, mirroring vulnerabilities detected weeks earlier in France by national cybersecurity agencies investigating intrusions into systems managed by Danfoss and Copeland.
Supermarket Chains Face Cyberattacks Affecting Refrigeration Systems
Which supermarket chains and brands have been affected by the refrigeration cyberattacks?
Confirmed impacted brands include Intermarché in Portugal, along with major international retailers such as Delhaize, Carrefour, Spar, Swedish chains ICA and Coop, and select Ikea stores operating across Belgium, Sweden, the Netherlands, Luxemburg, Ireland, Finland, and Estonia.
How were the refrigeration systems manipulated by the hackers?
Investigators report that malicious actors exploited remote access vulnerabilities in electronic temperature controllers. In numerous instances, hackers altered settings to push freezer temperatures up to 50 degrees Celsius, effectively disabling cold storage units and destroying fresh and frozen food inventories.
What specific European agencies are coordinating the response?
The European Commission has organized emergency response sessions through the European Union Agency for Cybersecurity (ENISA), Europol, and the EU-CyCLONe network, working alongside national law enforcement authorities in the eight affected countries.