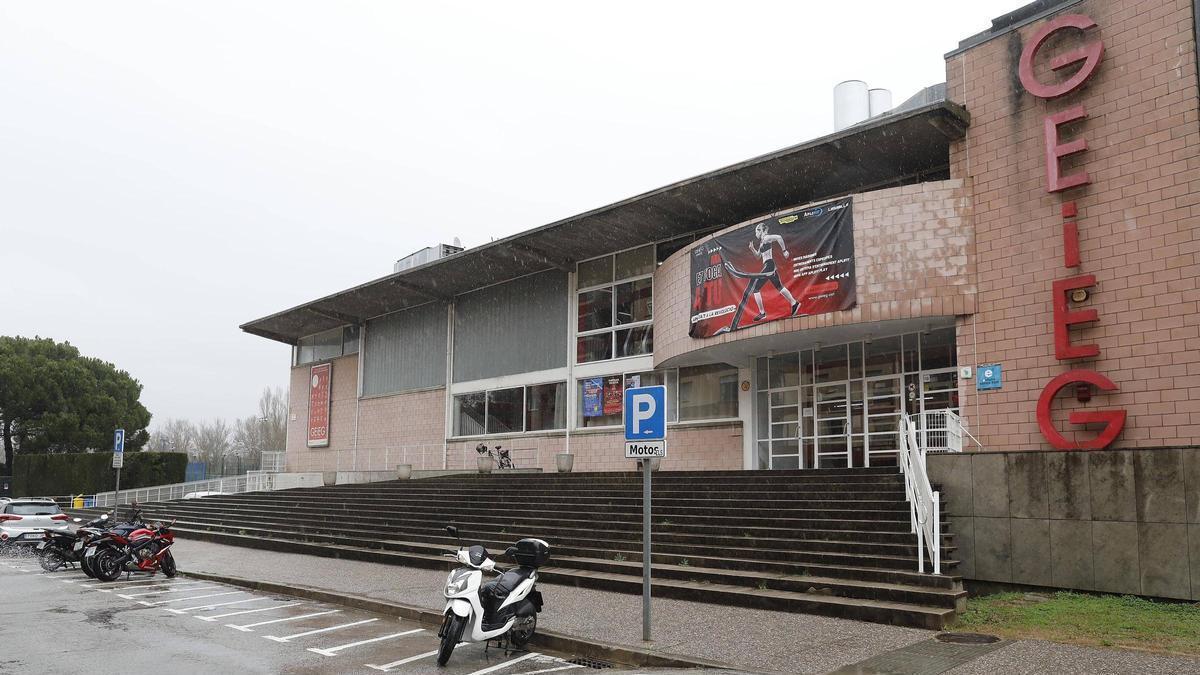
Grup Excursionista i Esportiu Gironí (GEiEG) disclosed a cyberattack suffered this September, warning its members that personal, financial, and health data may have been exposed. According to official club communications released over the weekend via email and its website, the organization is actively assessing the scope of the security breach while notifying affected stakeholders.
Immediate Security Notification Issued to Members
The sports club addressed its membership base following the September security incident, utilizing direct email alerts alongside an official statement posted to the institution’s primary web portal. Management confirmed that the breach compromised various categories of sensitive information belonging to members, athletes, employees, and commercial partners.
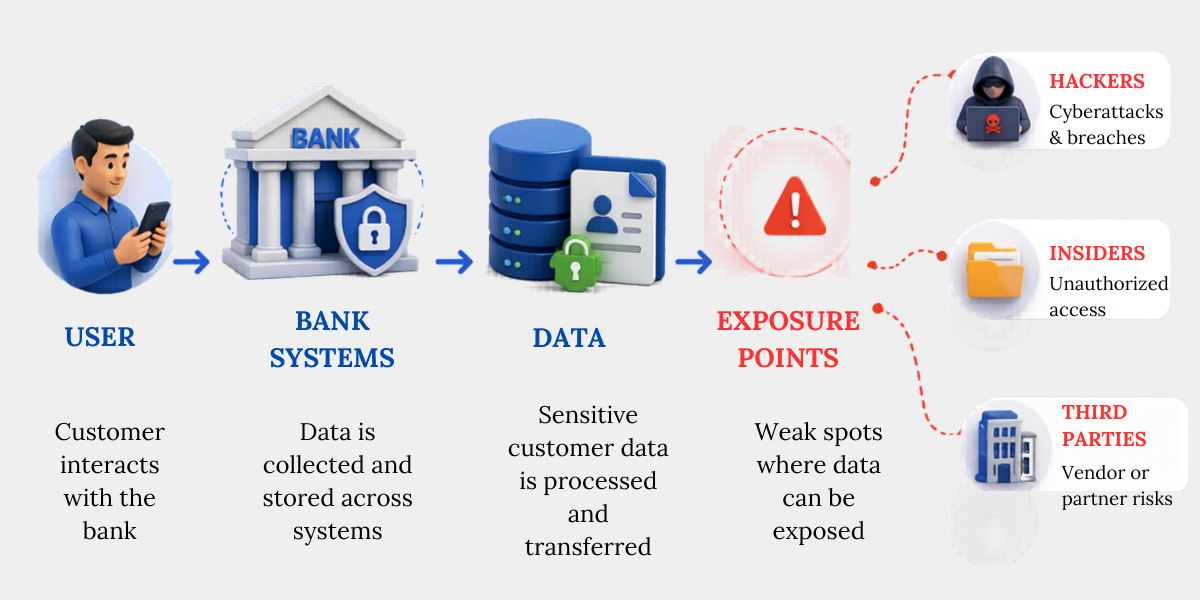
Club administrators outlined the specific data streams potentially affected by the unauthorized network access. According to the GEiEG statement, exposed records include standard identification and contact details, banking information, and health records linked to sports practice and participation in club-run activities.
Vulnerable Records Involving Minors and Workforce
The security incident extends beyond standard adult membership profiles, raising operational and privacy concerns for vulnerable groups within the organization. The club explicitly noted that data concerning minors has potentially been exposed as part of the cyber intrusion.
Labor Relations and Commercial Partner Exposure
In addition to youth and adult athlete records, the breach encompasses documentation related to the labor relations of the entity’s workforce and administrative employees. Commercial and contractual records tied to third-party suppliers, partners, and business associates doing business with the club also fall within the scope of the files accessed during the September attack.
Active Remediation and Stakeholder Guidance
Stakeholders seeking additional information can review the formal notice published on the official GEiEG web portal.
Worth a look