Alicante Teenager Arrested in International Sweep Over 1,000 Cyberattacks and Generalitat Hack
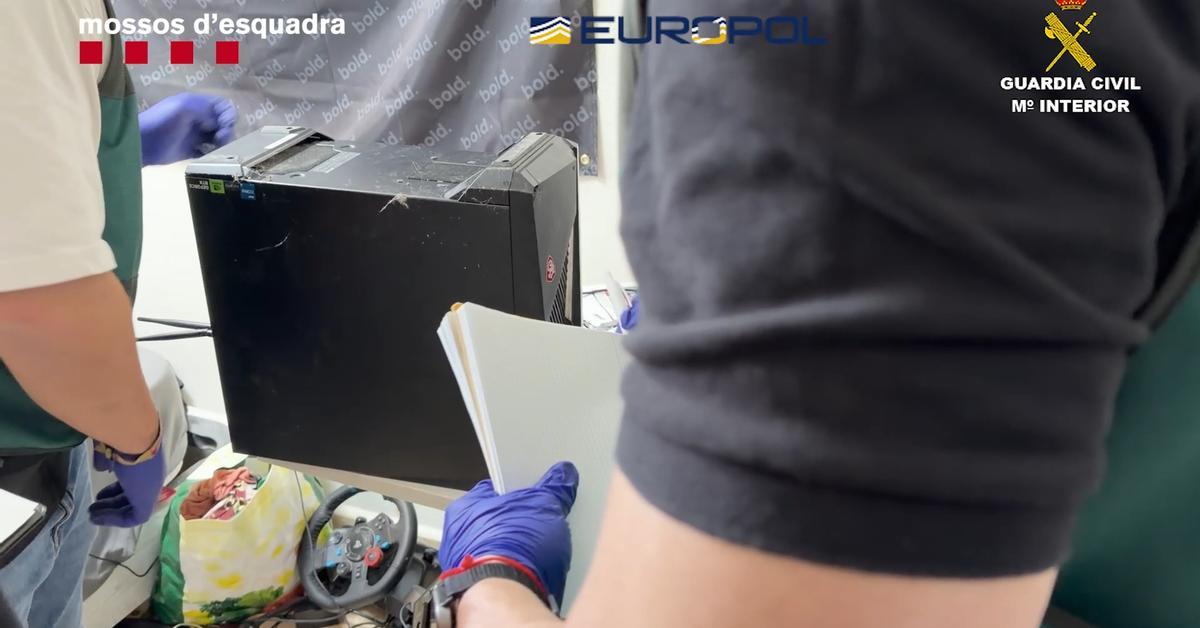
A 16-year-old boy operating from his bedroom in an Alicante home directed an international cybercriminal network responsible for more than 1,000 cyberattacks worldwide, according to an investigation by the Mossos d’Esquadra and the Guardia Civil. Working alongside Europol and the FBI, law enforcement agencies from nine countries dismantled the infrastructure of the ransomware group known as KillSec, arresting the minor alongside two other suspects in an operation that secured at least 1,100 terabytes of data.
How the KillSec Network Targeted Global Organizations
Active since approximately 2024, KillSec specialized in ransomware deployments and data extortion. The group exploited security vulnerabilities and poorly protected access points—particularly within storage environments and servers—to breach organizational systems. Once inside, members copied sensitive internal data, transferred it to infrastructure under their control, and listed victims on a dark web leak site. Organizations were then threatened with public data publication unless they paid ransom demands, which in some cases reached approximately 500,000 euros in cryptocurrencies.
The 2025 Cyberattack on Infraestructures.cat
Among the group’s high-profile targets was Infraestructures.cat, a public entity under the Generalitat de Catalunya, which suffered a devastating cyberattack early last year that caused damages approaching one million euros. The breach initiated the Mossos d’Esquadra investigation after hackers accessed company systems, stole sensitive information, and attempted extortion. Institution representatives confirmed that security measures have since been significantly reinforced.
Joint Law Enforcement Operation Across Nine Countries
The dismantling of KillSec followed a dual investigative track. Following the Catalonia breach, the Mossos d’Esquadra pursued the regional angles. Concurrently, the Guardia Civil launched a separate probe following a collaboration request from the FBI in San Juan, Puerto Rico, aimed at identifying Spain-based individuals connected to KillSec. Investigators utilized a profile image to identify the young administrator residing in the province of Alicante, leading to a joint investigative task force between the two Spanish police forces. The broader international operation involved authorities from Belgium, Finland, Germany, Greece, Romania, Spain, Switzerland, the United Kingdom, and the United States.
Dismantling Central Servers and Dark Web Leaks
During the coordinated raid, law enforcement successfully neutralized KillSec’s infrastructure, including its dedicated dark web leak page. Police placed five central servers under official control and seized multiple internet domains. Out of the roughly 1,000 total attacks attributed to the group globally, approximately 500 succeeded, accumulating a victim count exceeding 280 entities.
What Software and Payments Characterized KillSec Attacks?
What software did KillSec use to execute their extortion campaigns?
The network deployed malicious software known as ransomware, alongside customized data-theft scripts designed to infiltrate poorly secured servers and storage environments.
How much did victims typically pay to recover stolen data?
Investigators noted that certain victimized organizations paid ransom demands hovering around 500,000 euros paid entirely in cryptocurrency.
Which international agencies assisted Spanish police in the arrest?
The operation was supported by Europol, the FBI, and police authorities from Belgium, Finland, Germany, Greece, Romania, Switzerland, and the United Kingdom.
Keep reading